Offensive Security Partner
Unexploitable by
thorough testing.
We simulate real-world attacks to uncover vulnerabilities, prove their impact, and help your team fix them before attackers do.
- NDA first
- Controlled testing
- Clear, actionable reports
Trusted by forward-thinking organizations
- Fintech & Banking
- E-commerce
- SaaS & Software
- Healthcare
- Telecom
- Government
- Education
- Startups
Testing aligned with PCI DSS · ISO 27001 · SOC 2 · HIPAA · GDPR
Our Services
Full-spectrum offensive security.
From web and mobile to cloud and people, we help you find and fix real risks before attackers do.
Web Application VAPT
OWASP-driven testing that finds what scanners miss.
API Security Testing
REST, GraphQL, SOAP: broken auth, BOLA and more.
Mobile App Security
Android and iOS: storage, traffic, binary, and backend.
Network Security Assessment
From exposed ports to full domain compromise.
Cloud Security Assessment
AWS, Azure, GCP: secure your cloud infrastructure.
Red Teaming
Realistic, goal-based attack simulations.
Digital Forensics & Incident Response
Investigate, contain and recover.
OSINT & Threat Intelligence
Actionable intelligence for better decisions.
Source Code Review
Manual and automated review to uncover security flaws that black-box testing can miss.
AI/LLM Security Testing
Assess AI applications and LLM integrations for prompt injection, data leakage, unsafe outputs, and abuse paths.
Database Security Assessment
Assess database exposure, authentication, permissions, configuration, and access controls.
Also available — Vulnerability Assessment · Security Consulting · Active Directory · Social Engineering · Wireless · Compliance-Aligned Testing · Continuous Testing (PTaaS)
Our Process
A clear, collaborative process.
Structured. Transparent. Built around your goals.
No surprises. Just results.
- 01
Scope & Plan
Define objectives, coverage and rules of engagement.
- 02
Test & Exploit
Manual-first testing with real-world methodologies.
- 03
Report & Remediate
Clear, evidence-based findings with actionable fixes.
- 04
Retest & Close
We verify your fixes and help you strengthen your defenses.
Why Us
Built to break in.
Written to help you fix.
We attack your systems first, so nobody else can under NDA, inside agreed rules of engagement, with proof for every claim.
- A
Manual-first testing
Automation finds noise. We find the chains.
- B
Proof, not guesses
Every finding ships with reproducible evidence.
- C
Fixes developers can use
Prioritized by real business impact.
- D
Retest included
We verify your fixes, not just report them.
- E
Safe and confidential
NDA, rules of engagement, controlled testing.
Case Studies
Real-world results.
Stronger, safer businesses.
See how we've helped organizations identify critical risks, fix them, and build stronger security foundations.
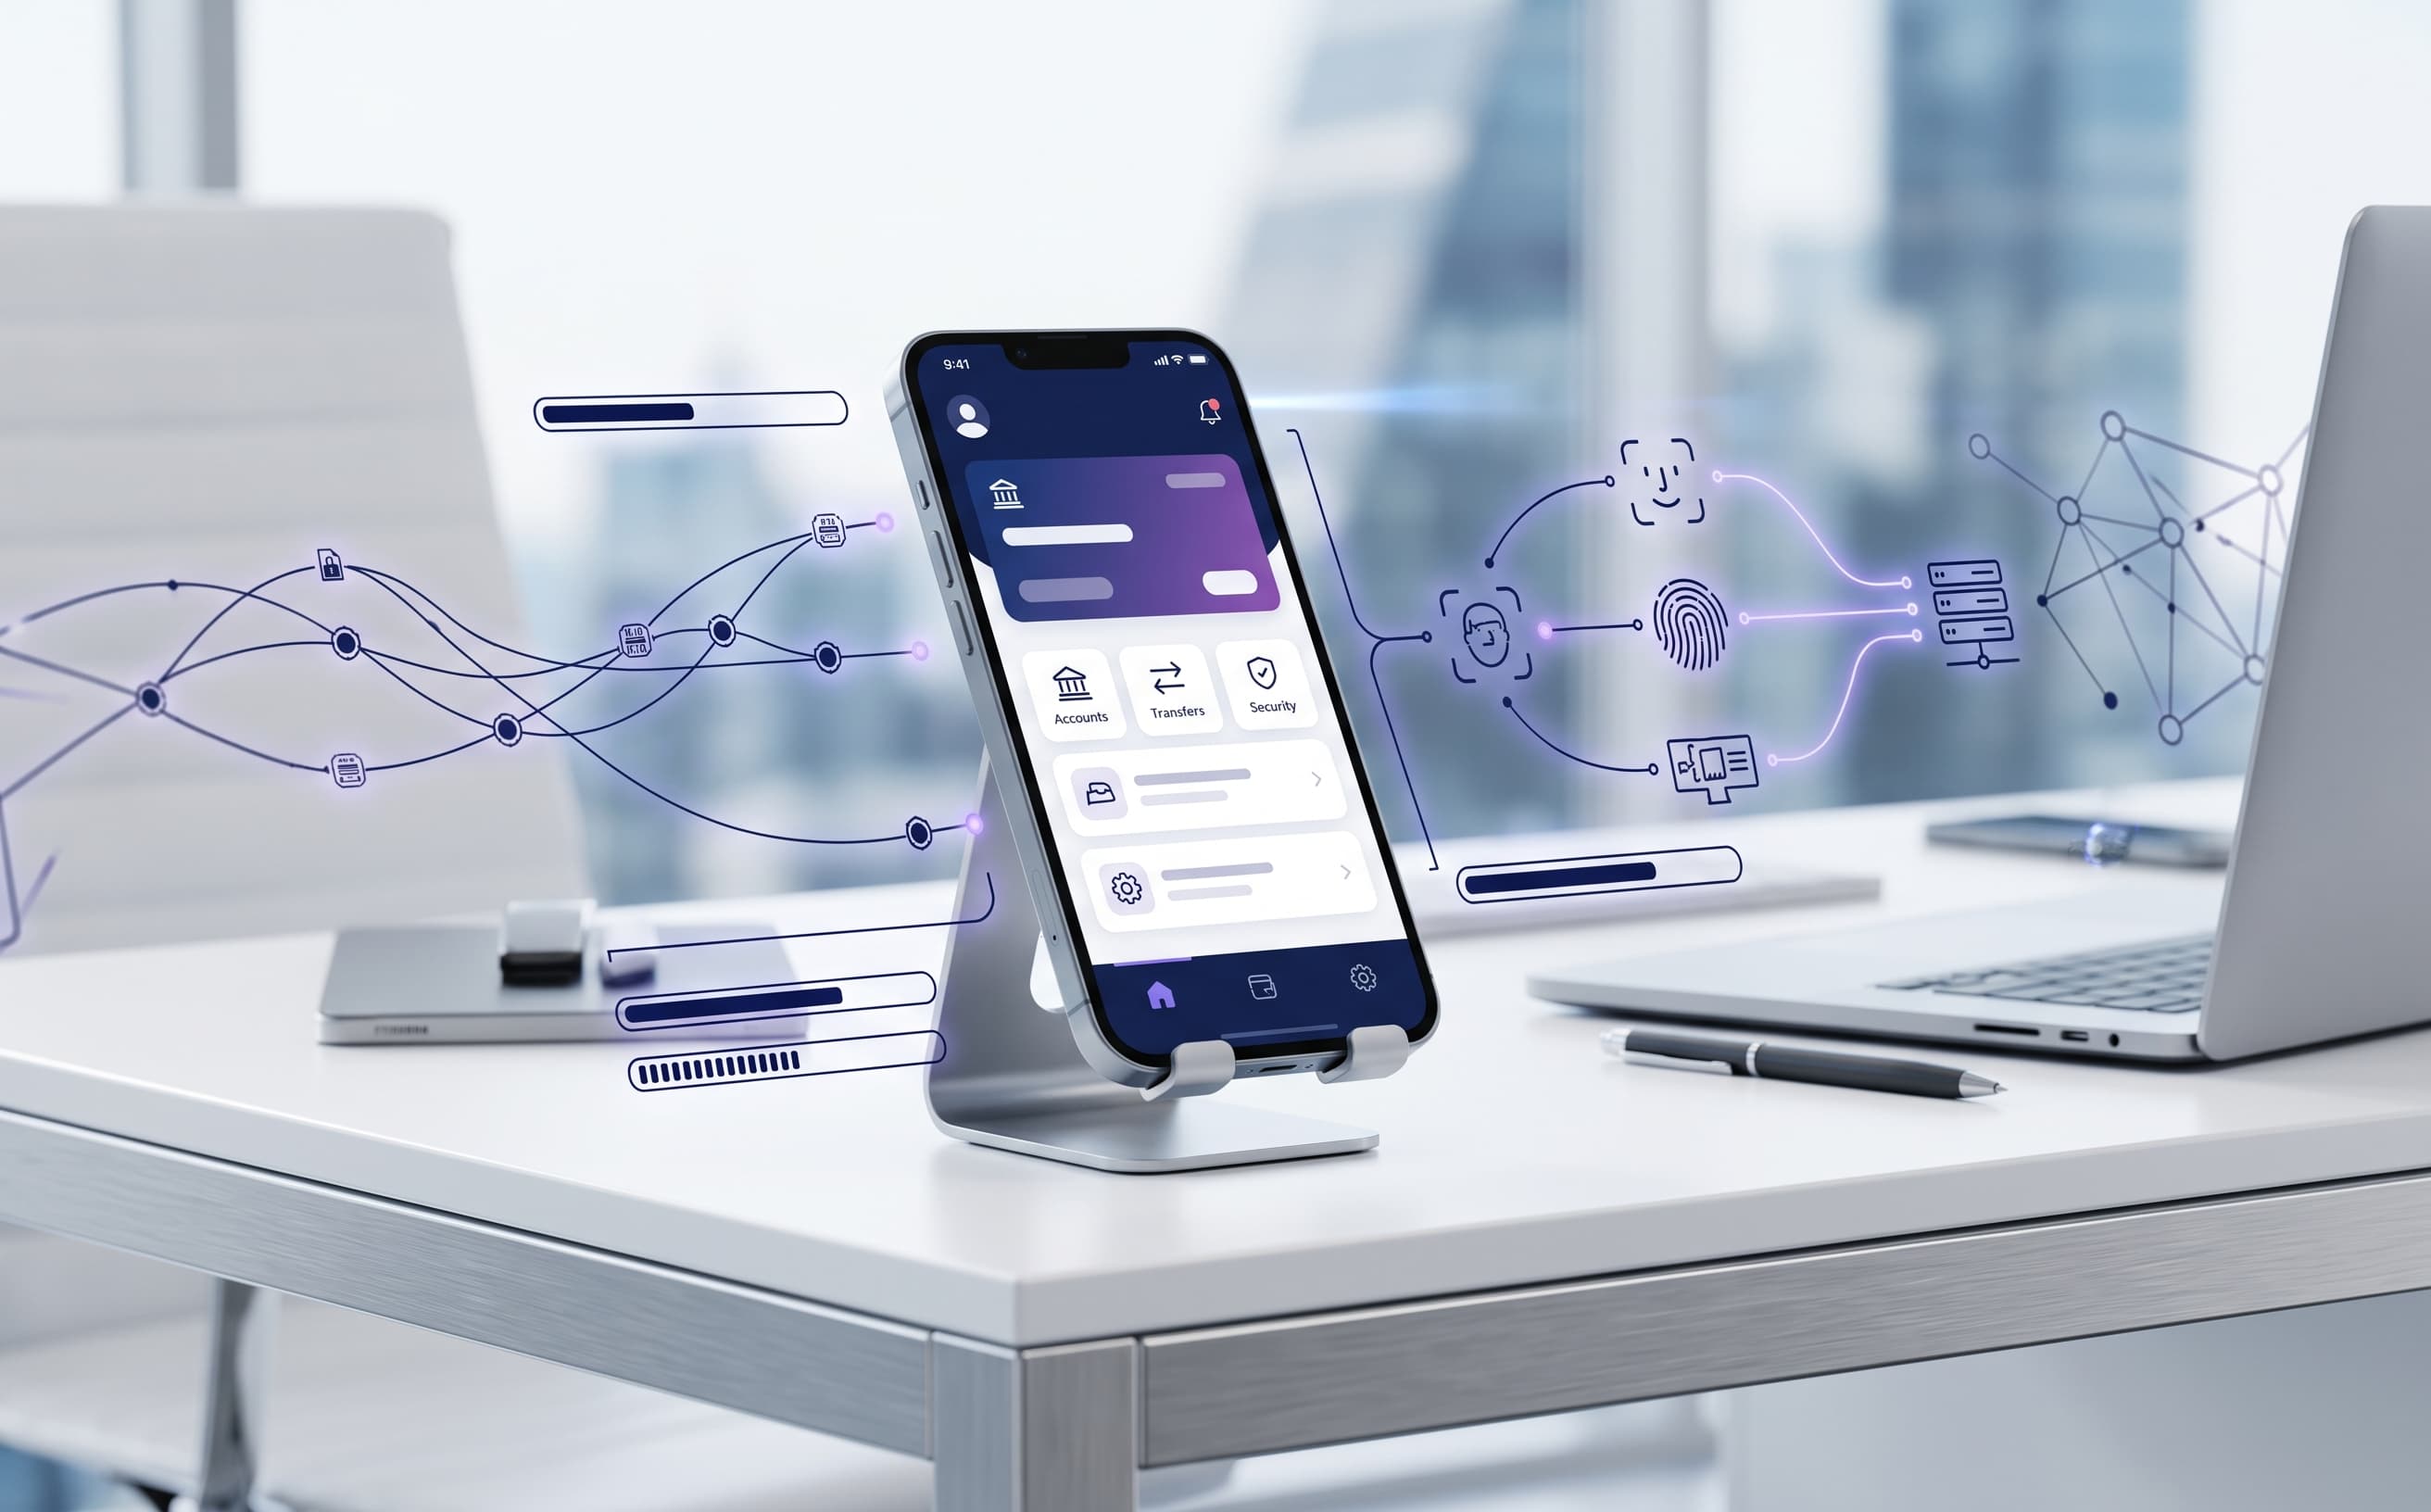 Mobile VAPT
Bypassing SSL Pinning Without Frida on a Regional Fintech App
An arm64-only Flutter build with SSL pinning was decrypted end-to-end using only network-layer tricks — no memory hooking required.Read case study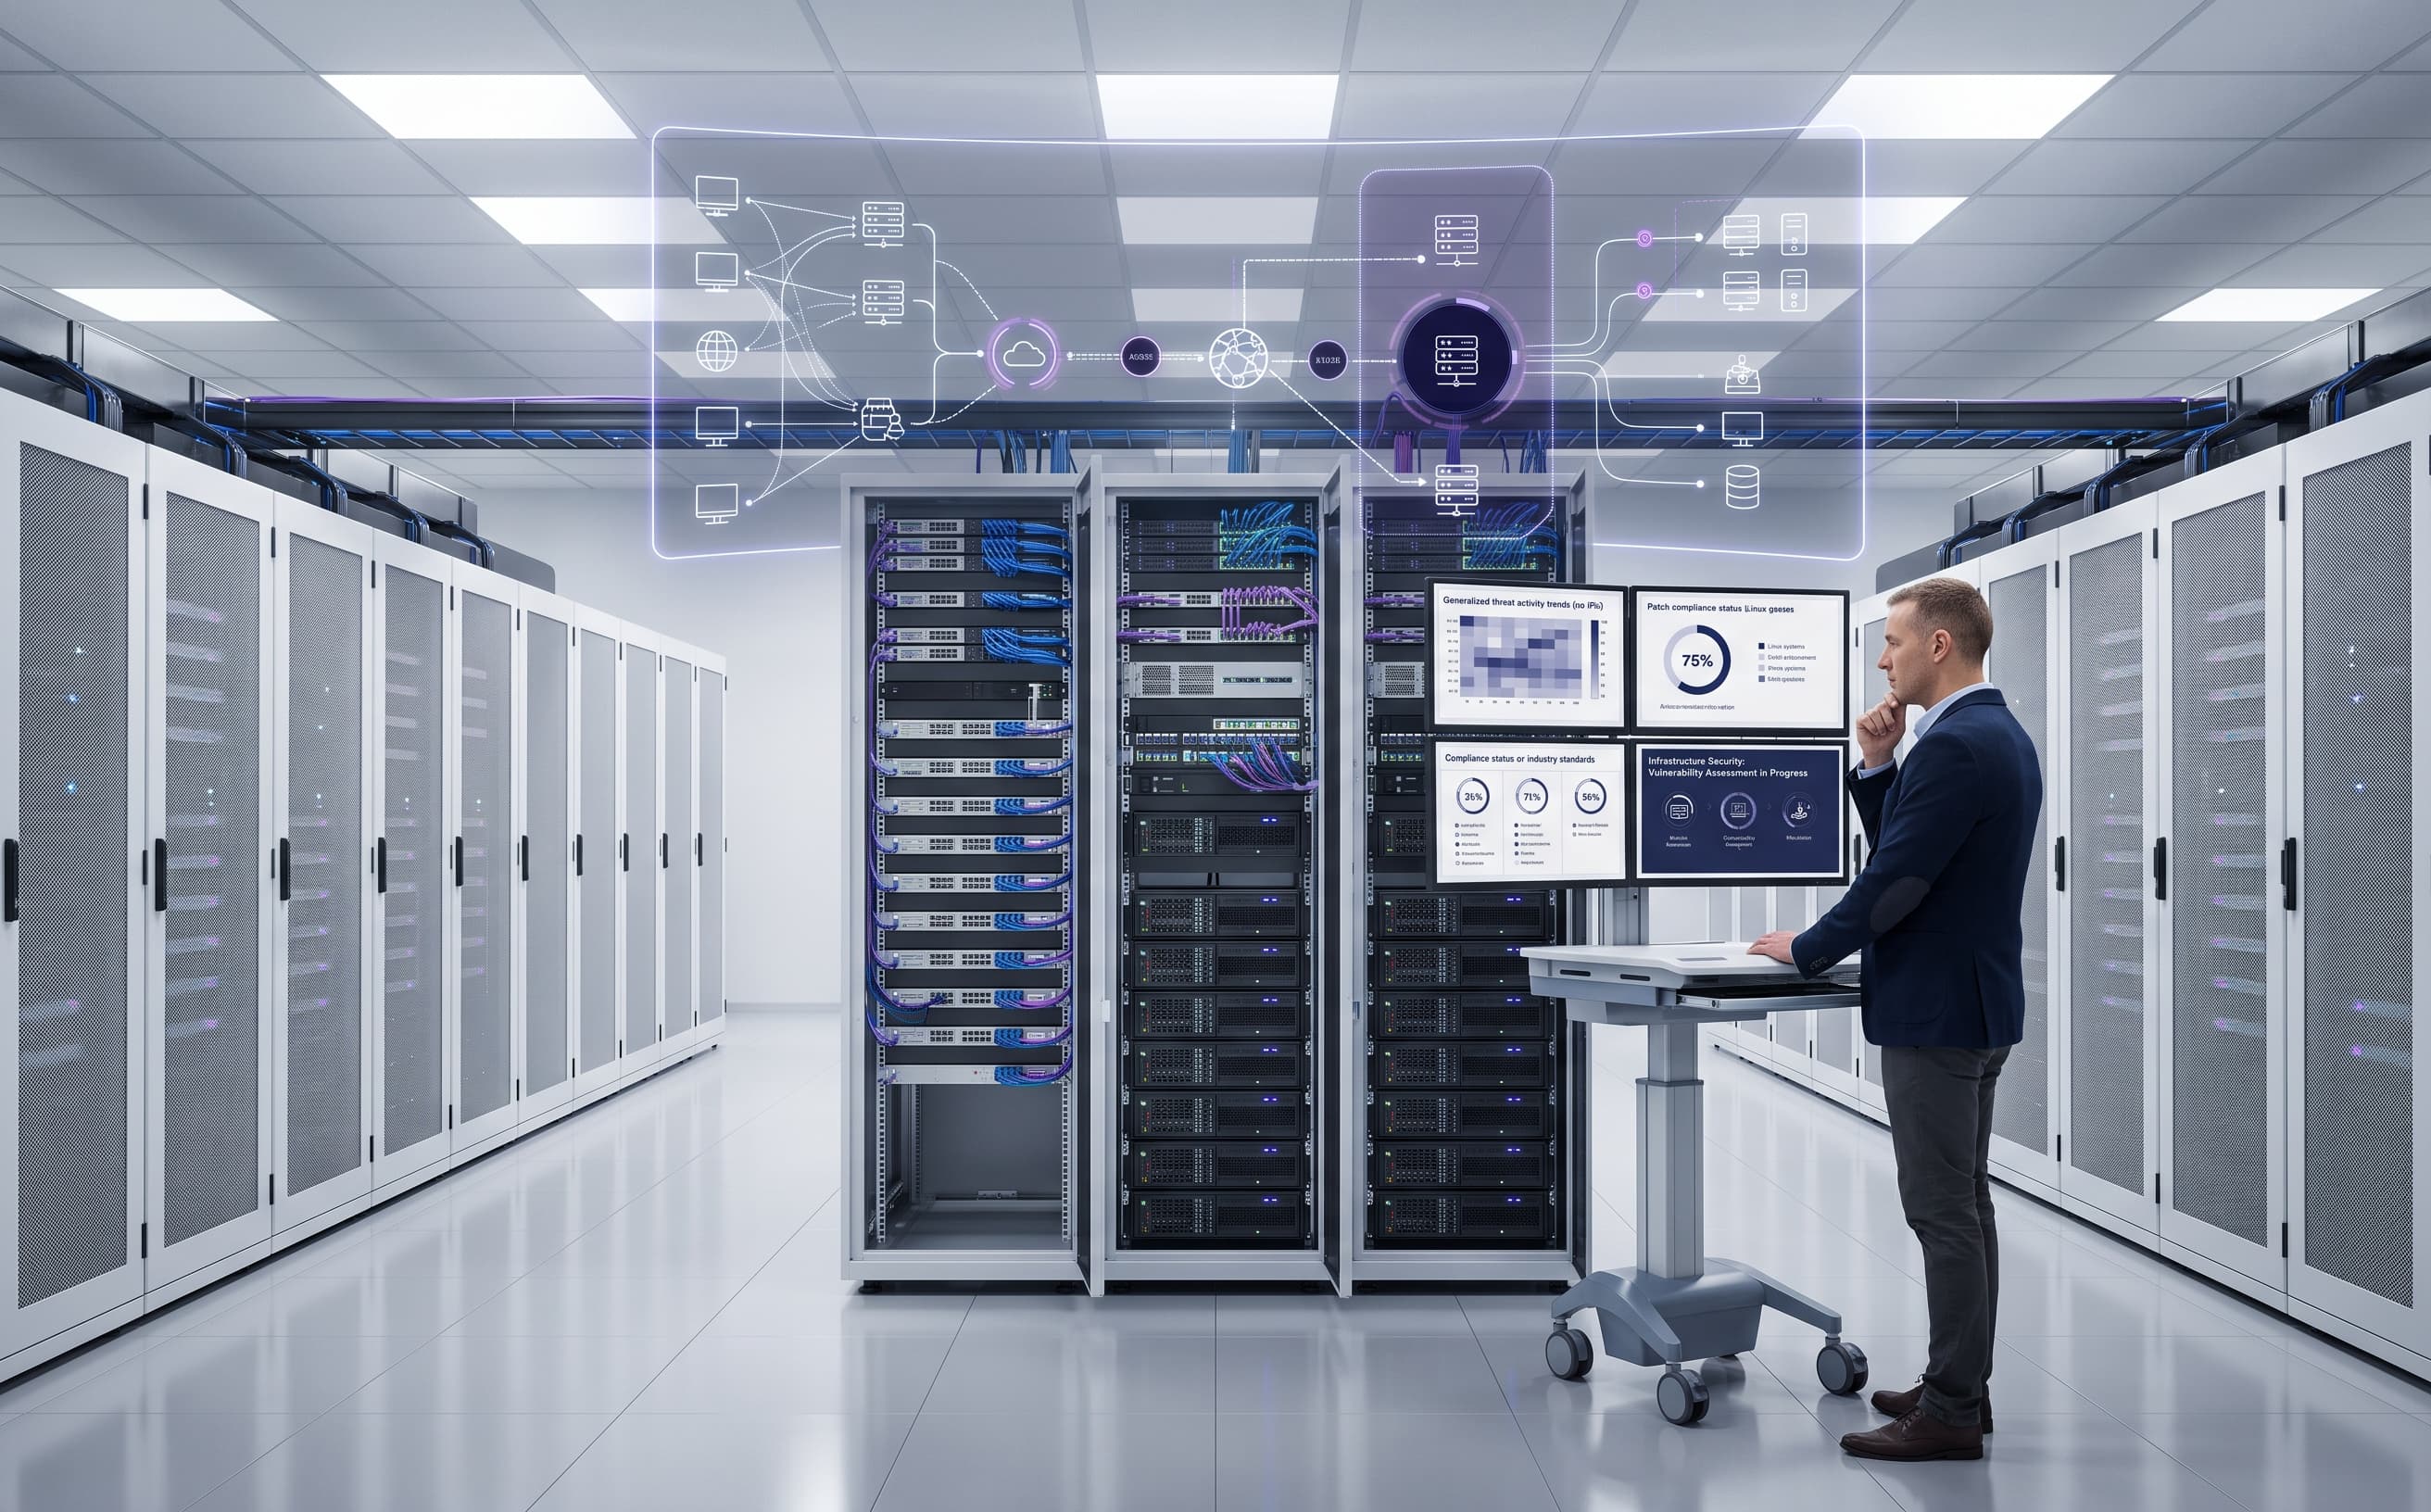 Infrastructure
From a Default Password to Full Root on Banking Time Infrastructure
A weak administrative credential and missing lockout controls created a direct path to privileged access on a bank's NTP infrastructure.Read case study Web VAPT
Logout That Doesn't Log You Out: Session Flaws on a Healthcare Platform
Password changes and logout failed to invalidate active authentication sessions, leaving previously issued access tokens usable.Read case study
What Clients Say
Trusted by security
and engineering leaders.
Real feedback from real clients.
“We assigned them blackbox testing for our assets. They delivered legitimate, high-value findings within the committed time. The report was clear and actionable.”
Muhammad AnsarCTO & Co-founder, SignX “They did pentesting for our AI-based software and found critical loopholes our developers had missed. Excellent technical depth and real value.”
Manzar AliSoftware Engineer, AI Product Company “We had a case involving a fake profile and impersonation. They conducted a detailed OSINT investigation, traced digital footprints and helped identify the person behind the profile. Professional, confidential, and well-documented work.”
Anonymous ClientFreelance Project - OSINT Investigation
Get a Quote
Let's make your business unexploitable.
Tell us about your security needs and we'll get back to you shortly.
- NDA first
- No obligation
- Tailored to your environment
- Talk to real security experts
Frequently Asked Questions
Straight answers.
Everything you need to know before getting started.
No. We agree rules of engagement before anything starts, test inside defined windows, and use controlled techniques. Anything with real risk is discussed with you before we attempt it, and we stay reachable throughout the engagement.
A scanner lists what might be wrong. We prove what actually is. Our testers manually verify every finding, chain issues together the way a real attacker would, and strip out the false positives a scan leaves in your backlog.
It depends on scope: the number of applications, endpoints, user roles and environments in play. After a short scoping call we give you a firm timeline and a fixed scope in writing, so there are no moving targets once testing starts.
Yes, and we sign it before scoping. Findings are shared only with the people you name. We test only systems you own or have explicit written authority to test, and every engagement is documented.
We run testing and reporting aligned with PCI DSS, ISO 27001, SOC 2, HIPAA and GDPR expectations, so you have audit-ready evidence. We are a testing partner, not a certification body: we help you gather what your auditor asks for, so you can demonstrate compliance more easily.