Technical Overview
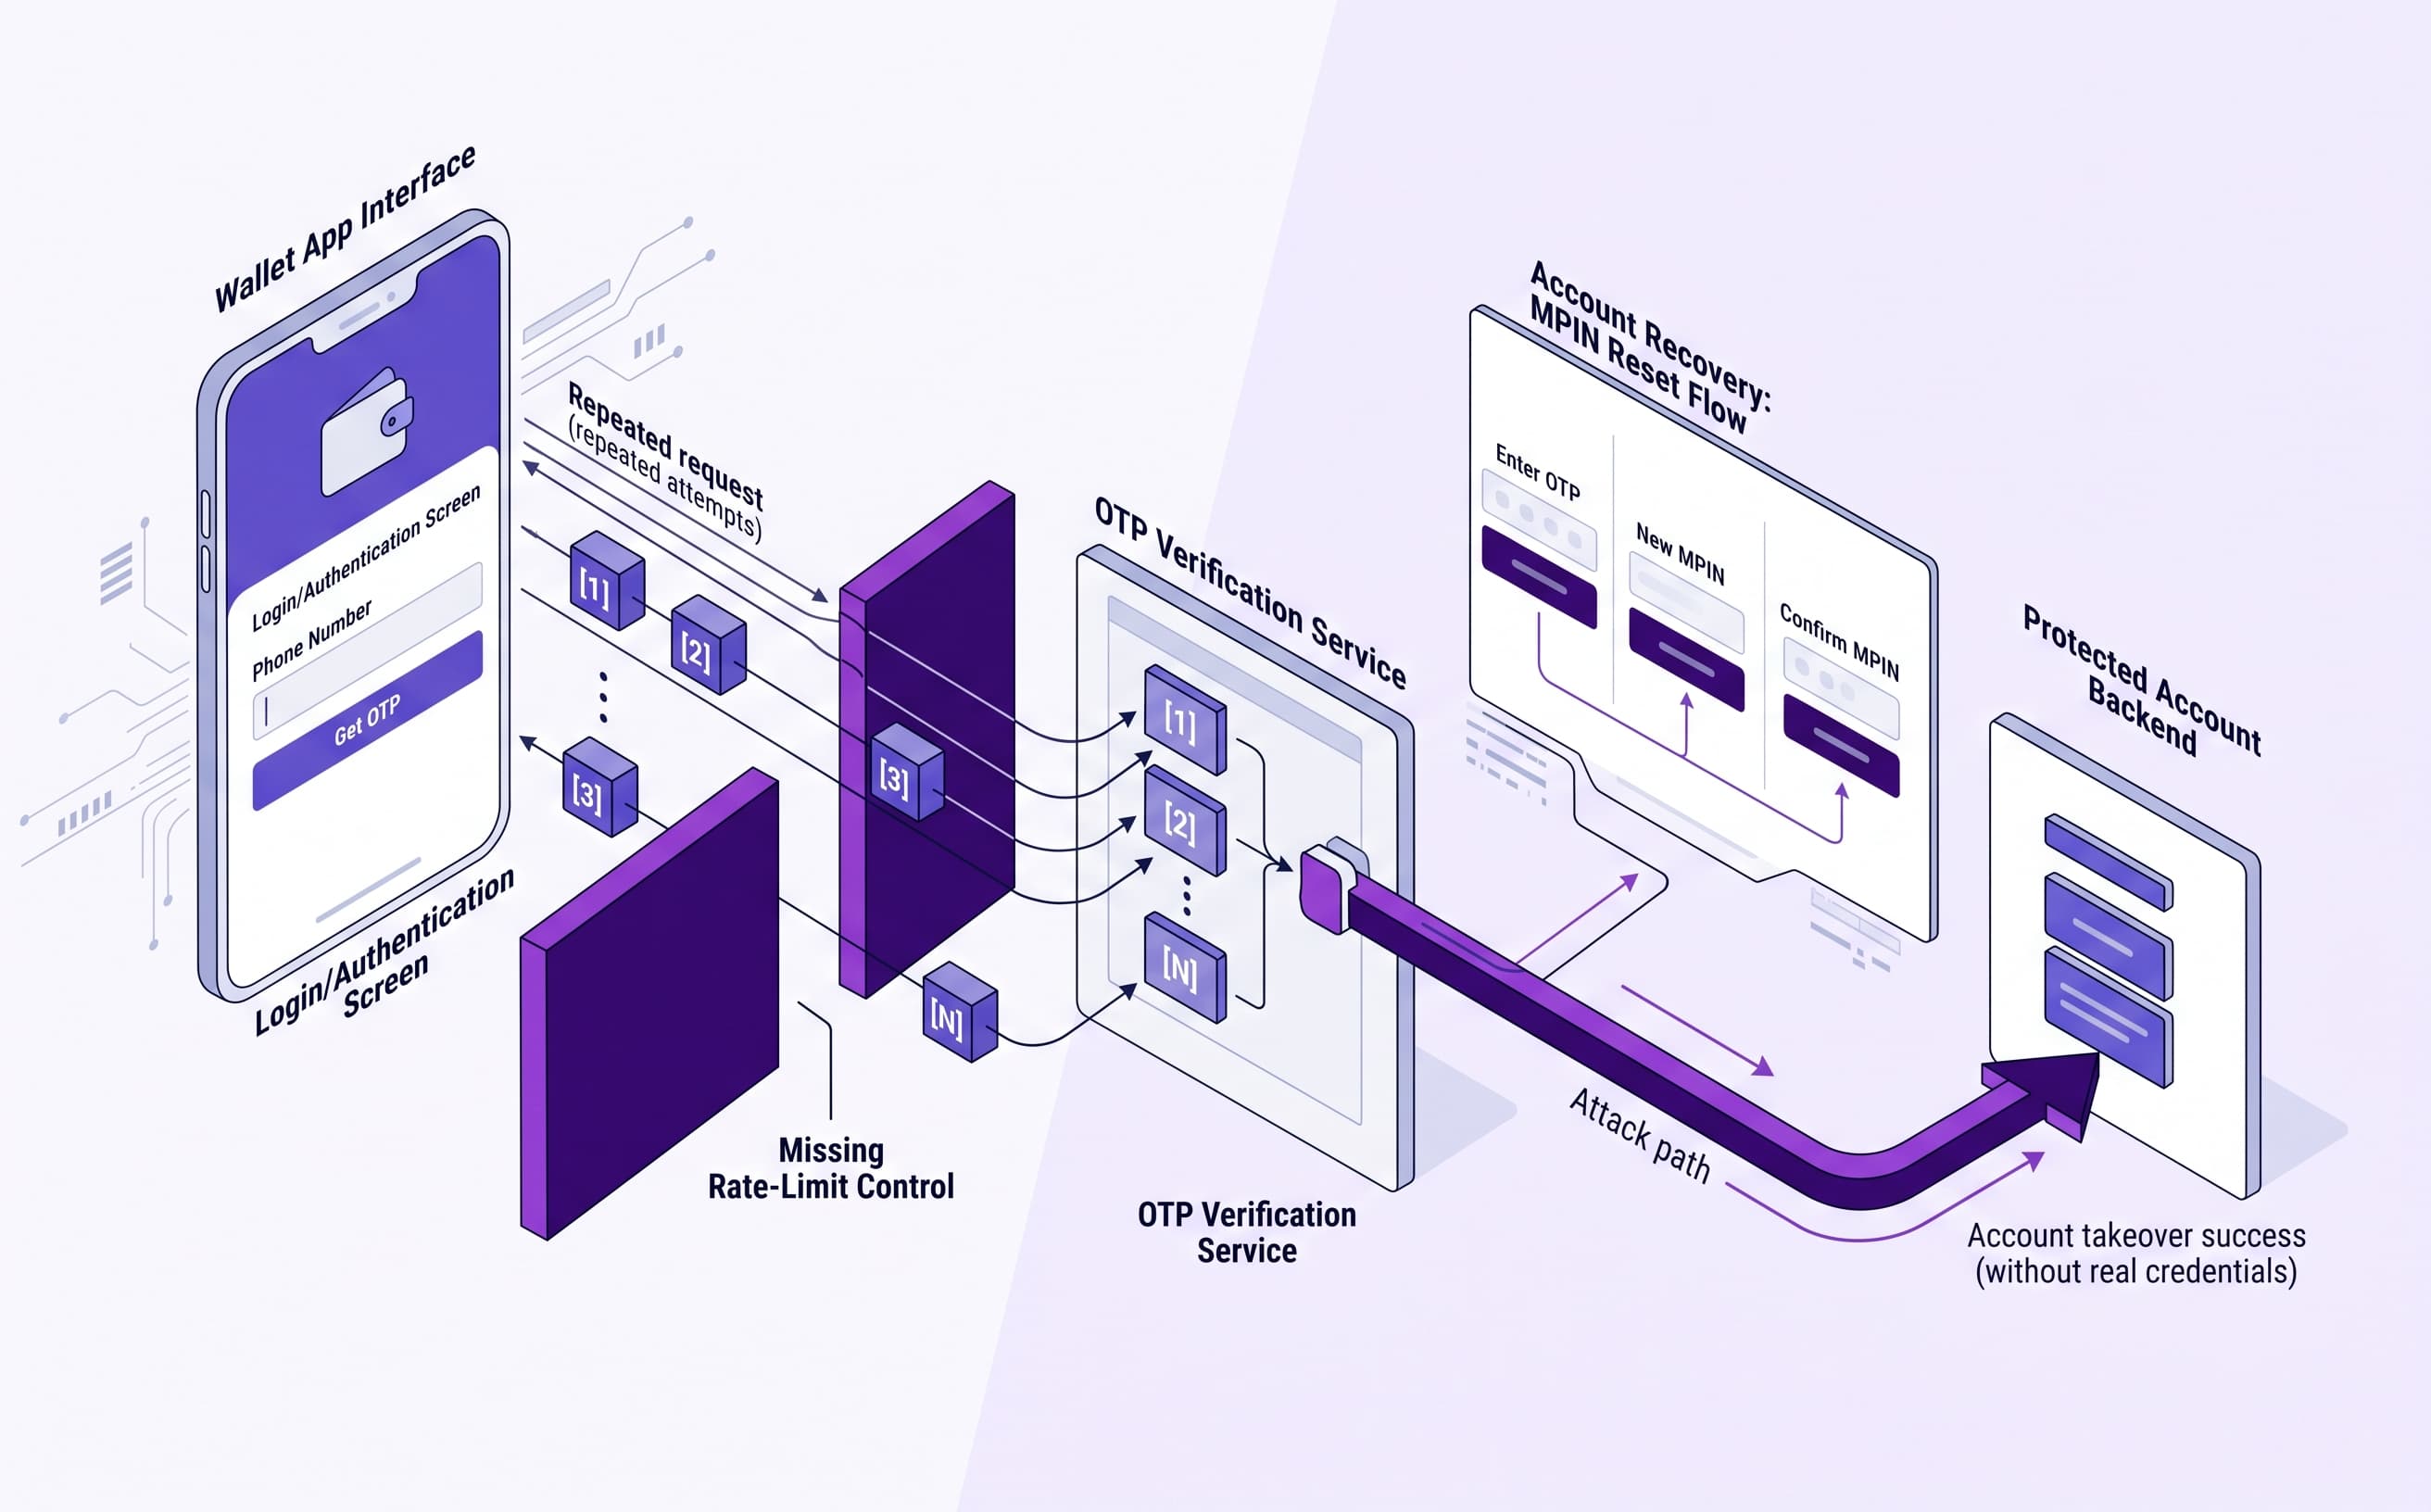
The OTP verification endpoint lacked effective rate limiting and lockout controls.
The application's responses also provided distinguishable behavior between unsuccessful and successful verification attempts, creating an additional signal that could assist automated guessing.
After successful verification, the account recovery flow did not provide sufficient additional verification before allowing a sensitive account credential change.
Impact
Weak OTP protections combined with insufficient account-recovery controls created a potential path to account takeover.
Recommendation
Rate-limit and lock out repeated OTP attempts, standardize authentication responses, monitor abnormal verification activity, and require fresh verification before sensitive account recovery actions.
Need an assessment?
Find the weaknesses before someone else does.
Tell us what you're building, what you're protecting, or what you're concerned about. We'll help identify the appropriate security assessment.
Request an assessment